Note: Should you wish to suggest an improvement or simply get in touch, you can reach me at contact@lionsec.lu.
In the very beginning
It was the early 2000s, and it was before my amazed teenage eyes — as I was just beginning to discover the world of Hacking (interwoven with (too) many hours of Quake III Arena) — that I discovered the site Milw0rm.com, one of the most popular sites of the era, publishing vulnerabilities and exploits to the general public.
Its lime-green and black design (which also inspired the main theme of this portfolio) revealed to me the richness of this world — all those exploits, those techniques. I understood absolutely nothing of it. And yet it is one of the relics that shaped my beginnings, much like the Phrack site, still active today. And for those who remember, the phpBB CVE-2005-0614 was behind a few good laughs.
Milw0rm was not the only one; others existed, such as FrSIRT (which became VUPEN, then Zerodium (shut down in 2024)), Packet Storm and SecurityFocus.
Back then (not so long ago when you think about it), before the GDPR, Root-Me or HackTheBox even existed, the cybersecurity industry as we know it today was still in its infancy. I’ll go even further: XSS was not yet recognised as a proven risk and was still a matter of debate (I’ll come back to this point later).
In short, it was the Wild West era, and it is to this site that I wish to pay tribute through this article.
The Milw0rm site
The site was launched in 2004 by an individual named str0ke (who proudly carried the prestigious title of Hacker), then shut down for good in 2010. Its name comes from the word mealworm (ver de farine in French).
It’s worth knowing that Milw0rm was first and foremost the name of a group of hacktivists (of which str0ke was a member under the alias Keystroke) that breached the BARC — an atomic research centre in Mumbai, India — in 1998. The Wikipedia page notes that the Milw0rm site, despite sharing the name, is not affiliated with the group.
Here is what the site looked like before it closed:
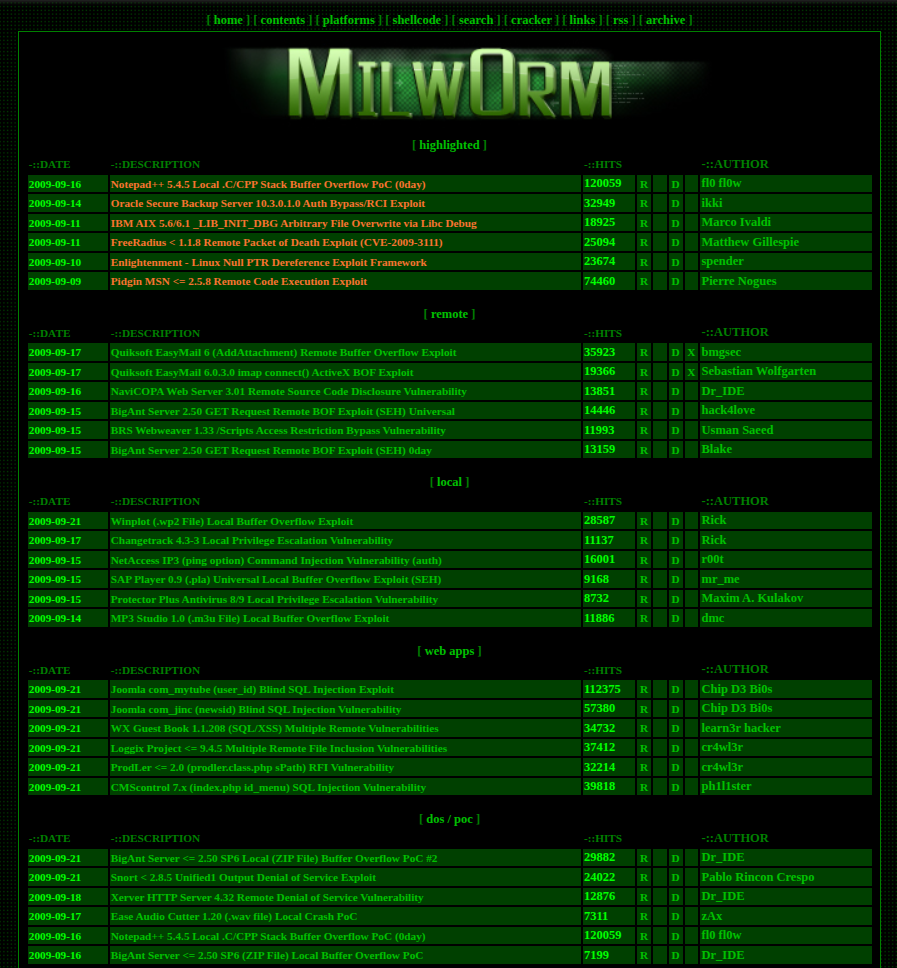
If the image rings a bell, yes — it really is the ancestor of Exploit-DB, as confirmed by this page archived by the WaybackMachine of Exploit-DB’s history. On 16 November 2009, OffSec took over Milw0rm’s database (Milw0rm had stopped accepting submissions from September 2009), and the site went live on 17 November, the day after.
The site featured many exploits (manually verified by str0ke himself), organised into the following sections:
- System / client exploits: remote and local
- Web applications
- Denial of service and Proofs of Concept
- Shellcodes: a small piece of machine code used to spawn a shell, run a command, download a file, etc.
- Papers: written tutorials in several languages
- Videos: video demonstrations of attacks
The site also featured an MD5 and LM hash cracker:
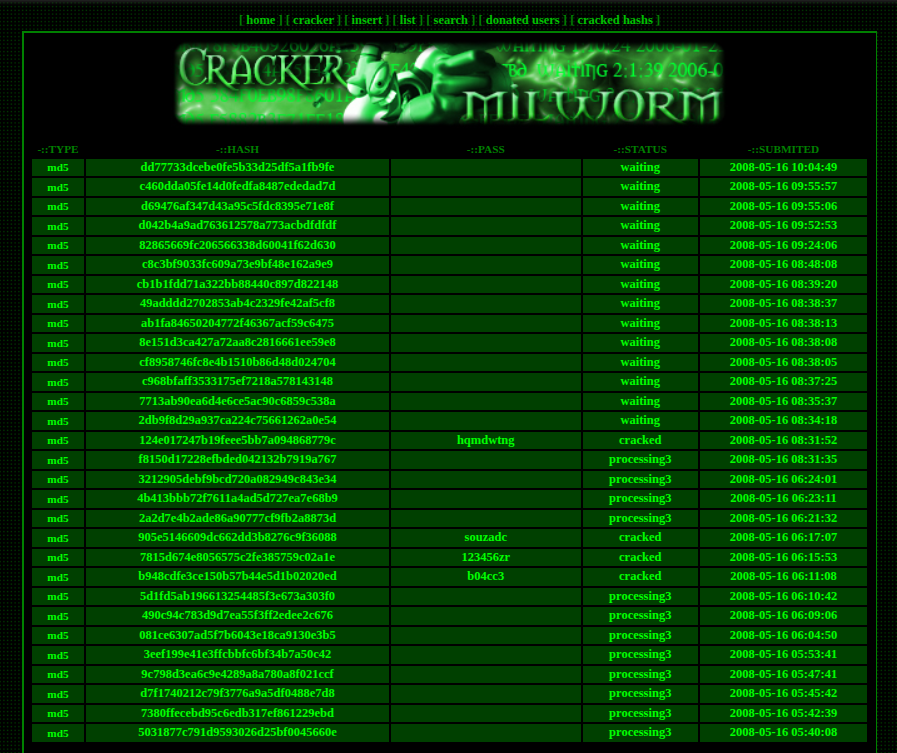
You could say str0ke had a real sense of service!
Special mention: rgod
Looking at the names attached to the exploits, one came up again and again: rgod, who already seemed very active from 2005 onward. And to my surprise, he still is in 2026! His exploits from back then are still available via his Exploit-DB profile, and he has more than 3,000 vulnerabilities to his name.
He found vulnerabilities in many major vendors such as Schneider Electric, Dassault Systèmes, LG, Adobe, Siemens, SAP, Oracle, Microsoft, IBM, HP, VMware, Symantec and many more.
An absolutely impressive list.
The evolution of the logos
Here is the evolution of Milw0rm’s logos, except the last one, which appeared only briefly. The most popular was the third:
First contact with the admin
I remember the day I had discovered an XSS vulnerability (on a very popular site, though I can’t for the life of me remember which). I must have been 14 or 15, and, proud as can be, I rushed to submit it to str0ke by email.
He replied that XSS was not accepted on the site. It’s true that it was still debated — “it’s a real risk” versus “it’s not that dangerous” — a very different time indeed!
I replied by asking him a question or two about his experience (always curious by nature!), to which he answered something along the lines of “you were still in diapers while I was already hacking”.
A reply I took with plenty of humour, of course =]
His address was str0ke@milw0rm.com, and he always signed off his emails with Be safe, /str0ke.
The farewell message
For a long time I looked for the reason the site had ceased to exist — to the point of asking an OffSec member during my OSAI+ course on the official Discord. Although a staff member replied with interest, I got no answer. But this is where AI excels once again: I found this source on SecLists.
Here is the message str0ke published announcing the site’s imminent shutdown for lack of time — because yes, str0ke took the time to verify every exploit published. You could already feel the pace picking up, and I think we’ll all agree it has only grown since!
Well, this is my goodbye header for milw0rm. I wish I had the time I did
in the past to post exploits, I just don't :(. For the past 3 months I
have actually done a pretty crappy job of getting peoples work out fast
enough to be proud of, 0 to 72 hours (taking off weekends) isn't fair to
the authors on this site. I appreciate and thank everyone for their
support in the past.
Be safe, /str0ke
Farewell, str0ke, and thank you for all the work that Milw0rm represented. Although I ask nearly every cybersecurity expert around me about this relic of the past, everyone seems to have forgotten.
For my part, it will remain, with great nostalgia, as one of the first Hacking sites ever to cross my path.
Links
- Phrack website
- Packet Storm website
- SecurityFocus website
- Root-Me platform
- HackTheBox platform
- Official BARC website
- Milw0rm Wikipedia page
- Official Exploit-DB website
- Exploit-DB history archived by the WaybackMachine
- rgod’s personal site (retrogod)
- rgod’s Exploit-DB profile
- OSAI+ (AI-300) course by OffSec
- str0ke’s farewell message archived on SecLists
Contact
For any suggestions or simply to get in touch: contact@lionsec.lu.